
Current firewall shortlist at a glance
A useful comparison should be easy to scan, but a current shortlist also needs a stated basis instead of unexplained stars or a universal winner. These labels describe the strongest documented fit, not a laboratory ranking. Firewalla Gold Pro emphasizes guided operation, Netgate 4200 emphasizes detailed pfSense administration, and UniFi Cloud Gateway Fiber emphasizes an integrated UniFi environment. The right choice still depends on the operator, topology, enabled inspection, support expectation, and recovery plan.
| Gateway | Best documented fit | Key evidence | Main tradeoff to verify |
|---|---|---|---|
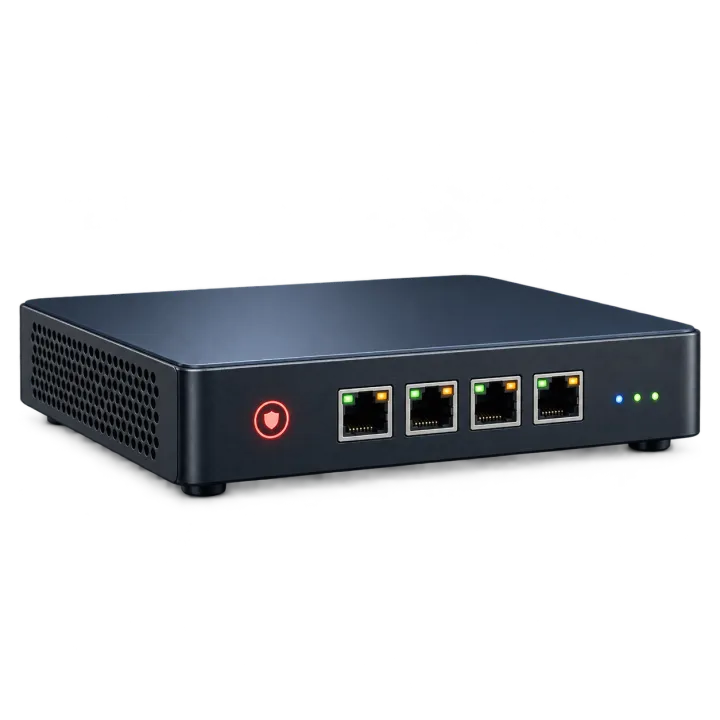
| Firewalla Gold Pro | Guided home or small-office policy management | Two 10 GbE and two 2.5 GbE interfaces; vendor states more than 10 Gbps packet processing | Phone-centered administration and the boundary between standard and optional business features |
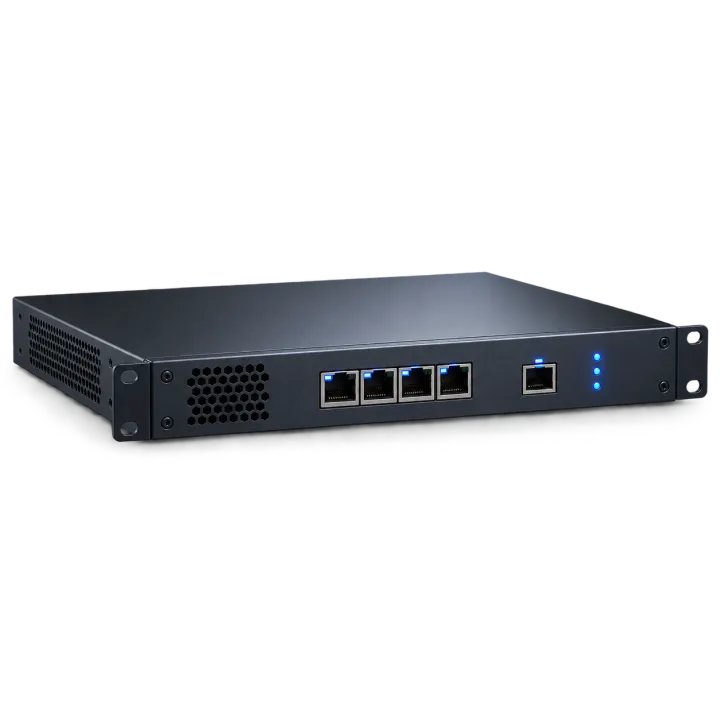
| Netgate 4200 | Detailed routing and firewall control on a supported pfSense appliance | Four 2.5 GbE interfaces, Intel Atom C1110, 4 GB memory, and 128 GB NVMe | Higher operator responsibility for policy, packages, upgrades, and recovery |
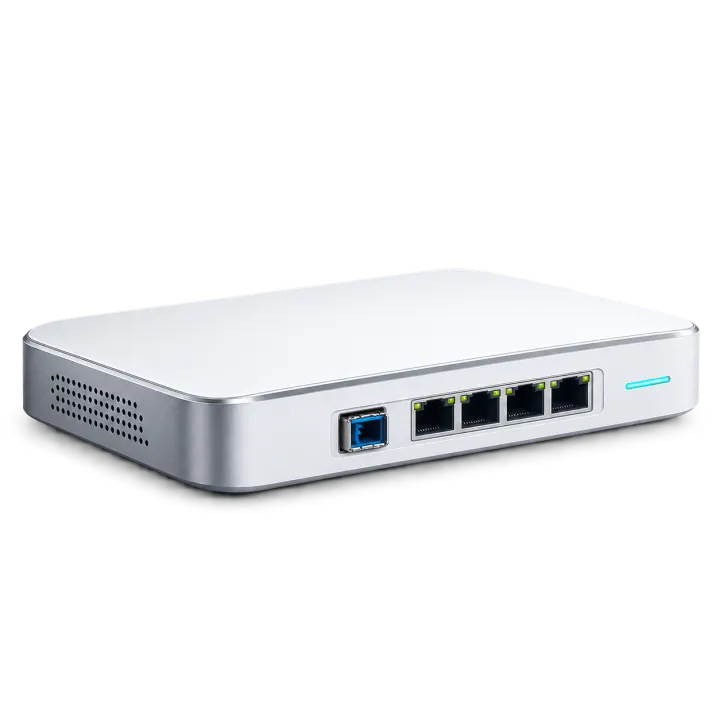
| UniFi Cloud Gateway Fiber | A network already using or planning UniFi management | 10G SFP+, 10 GbE, and vendor-rated 5 Gbps IDS or IPS | Ecosystem dependency, application scope, and feature-enabled capacity |
Firewalla Gold Pro review: guided operation
Firewalla Gold Pro is the most natural candidate here when the buyer values guided policy management, device visibility, approachable segmentation, and high-speed interfaces without wanting to operate a traditional firewall distribution. Its documented interface mix supports multi-gigabit network designs, but the physical ports alone do not prove that every inspection, VPN, queue, or logging workload will meet the same speed. Confirm how administration works during phone loss, account recovery, internet failure, and device replacement.
- Consider it when a small team needs understandable policy and device-level visibility.
- Verify optional business services, recurring costs, export, restore, and local recovery before purchase.
- Skip it when the required workflow depends on console-first administration or unsupported enterprise integrations.
Netgate 4200 review: detailed pfSense control
Netgate 4200 is the strongest fit in this shortlist for an operator who wants a supported appliance with detailed pfSense routing, firewall, VPN, diagnostics, and package choices. Four 2.5 GbE interfaces can support several physical boundaries without an immediate external switch, but interface count does not replace a topology plan. The flexibility has an operating cost: someone must understand rule order, packages, upgrades, certificates, logs, backups, and console recovery well enough to restore service safely.
- Consider it when the administrator already understands pfSense or has time to own the configuration.
- Verify package compatibility, remote support, console access, restore behavior, and feature-specific performance.
- Skip it when nobody can maintain a detailed gateway or recover it after a failed remote change.
UniFi Cloud Gateway Fiber review: one managed ecosystem
UniFi Cloud Gateway Fiber is the most coherent choice here when the network already uses UniFi switching, wireless access, cameras, or centralized administration. Its high-speed interfaces and published IDS or IPS figure make it attractive for a multi-gigabit design, but the value comes from the complete operating environment rather than one number. Confirm which UniFi applications will run, how storage and device limits apply, which security controls need subscriptions or companion products, and how configuration is recovered if the gateway fails.
- Consider it when unified network administration will reduce real operating effort.
- Verify application capacity, managed-device scale, failover needs, export, restore, and non-UniFi integration.
- Skip it when ecosystem dependence creates more cost or constraint than the consolidated management removes.
Treat published performance as a planning input
Vendor throughput figures are not interchangeable. One figure may describe basic routing, another packet processing, and another inspection with a named feature set. Encryption, intrusion prevention, traffic logging, application identification, VPN use, and traffic between internal zones can follow different processing paths. Record the exact vendor test description, then validate a candidate with the services and traffic pattern that will remain enabled in your network. Leave capacity for growth and for a failure mode that sends more traffic through one device.
- Separate internet, VPN, and inter-zone traffic requirements.
- Confirm whether the cited figure includes IDS, IPS, VPN, or other inspection.
- Check configuration export, local recovery, software support, replacement, and total recurring cost.
What this comparison can and cannot decide
This comparison can narrow the field by interfaces, documented performance, management model, ecosystem, support, and recovery requirements. It cannot reproduce the buyer's traffic, predict long-term reliability, verify detection quality, or prove that a default configuration is safe. A firewall also cannot replace supported endpoints, strong identity controls, application security, backups, incident response, or competent administration. Reject any candidate whose support horizon, feature-enabled capacity, recovery path, or total ownership cost cannot be documented before deployment.
Firewall gateway evidence matrix
Use one requirements sheet for every candidate. A blank cell is an evidence gap, not permission to assume the feature or capacity exists.
| Decision field | Evidence to preserve | Reject when |
|---|---|---|
| Interfaces | Exact port type, count, and intended WAN or LAN mapping | Adapters or switch design cannot meet the topology |
| Inspected capacity | Named feature set and published test conditions | Only an unqualified routing number is available |
| Operations | Administrator path, export, restore, console, logs | Recovery depends on the failed service |
| Lifecycle | Release policy, support route, subscriptions, replacement | No owner or supported horizon can be documented |
FirewallGuide checked the linked product documentation on October 31, 2026. Specifications and availability can change, so verify the final purchase against the vendor source.
How to select a gateway from documented evidence
Back up the old and new configurations, run business calls, transfers, VPN sessions, and guest isolation tests, then restore a known configuration. Preserve latency, throughput, CPU, log, and recovery evidence. Do not call the review complete after one internet speed test.
Example: replacing a gateway without buying from one benchmark
A small office has a 2 Gbps internet service, separate work and guest networks, six remote users, cloud backups, and no full-time network administrator. It wants inspection enabled but has not measured VPN or inter-zone traffic.
Choose only after documenting the operating owner
Measure the three traffic classes separately, identify who will operate the gateway, and eliminate any product whose management, recovery, support, or feature-enabled capacity does not fit. Request a return window or proof-of-concept where possible because published specifications cannot reproduce the office workload.
Current firewall review questions
Are these hands-on firewall reviews?
No. They are documented-capability reviews based on current official specifications and an operational requirements method. FirewallGuide states where independent lab evidence is absent.
Which firewall is best for every home?
None. Interface needs, operator skill, network design, support expectations, inspection load, and recovery requirements differ.
Can vendor throughput figures be compared directly?
Only when the traffic direction, packet size, features, protocol, and test method are equivalent. Preserve the exact test conditions with the number.
Current firewall comparison checklist
- Write the internet, VPN, and inter-zone requirements separately.
- Confirm ports, inspection limits, management dependency, backup, and local recovery.
- Price optional subscriptions, support, replacement, and required companion hardware.
- Record the vendor source and date for every decisive specification.
- Test the finalist with enabled features and a rollback plan.
Firewall review claims to reject
- Ranking a product from its largest throughput number without checking the traffic and feature conditions behind it.
- Treating a familiar brand or polished application as proof of support life, recovery quality, or security effectiveness.
- Publishing hands-on language when the evidence came only from vendor documentation.