
Hardware firewall throughput worksheet
Use measured traffic and enabled features instead of the largest number on a product sheet. Keep internet, VPN, and traffic between internal zones separate because each may use a different processing path.
| Workload | Current peak | Planning input |
|---|---|---|
| Internet download and upload | Measure both directions during a normal busy period | Required inspected WAN throughput |
| Remote access VPN | Count concurrent users and representative transfers | Encrypted throughput and authentication load |
| Traffic between zones | Measure backups, file access, cameras, and management | Internal policy throughput |
| Availability | Record tolerated outage and recovery time | Spare unit, failover, backup, and restore needs |
A home may need one supported gateway with reliable recovery. An office may also need centralized logs, identity integration, failover, multiple administrators, change approval, and vendor support.
Size the real path
Encrypted inspection, intrusion prevention, VPN use, and logging can reduce throughput. Write down internet speed, internal inter-segment traffic, concurrent users, and availability needs before comparing appliances.
Measure the busiest realistic path with the security functions you plan to enable. Internet speed alone misses traffic between VLANs, remote-access VPN load, encrypted inspection, and simultaneous users. Keep capacity for growth and failure conditions so a protective feature is not disabled later to restore performance.
- Check supported software and end-of-life dates.
- Confirm configuration export and restore.
- Verify that VLAN or zone policy is available if segmentation is a goal.
Separate capabilities that are often bundled
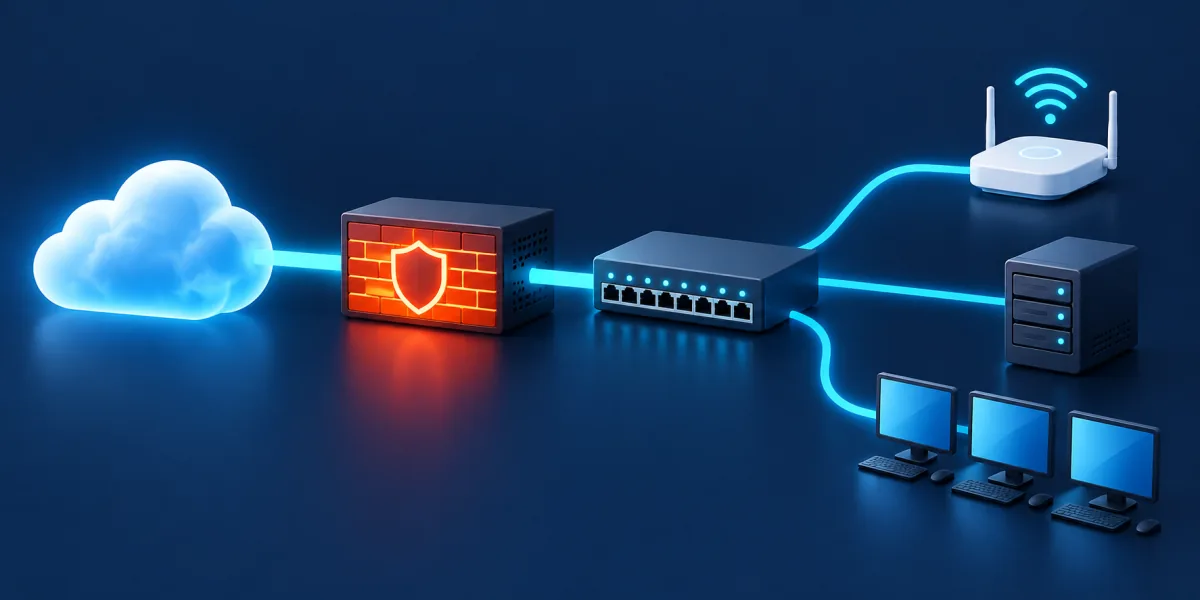
Ask where every function runs and who updates it. Routing, wireless access, switching, filtering, VPN, and identity services may be in one appliance or spread across several systems. The design is maintainable when a failure can be isolated and each configuration has a known backup and owner.
| Capability | Question to ask | Evidence |
|---|---|---|
| Firewall | Can rules express the required source, destination, service, and direction? | Administration guide and rule export |
| VPN | Which protocols, identities, and MFA methods are supported? | Current compatibility documentation |
| Threat inspection | What traffic is inspected and what is encrypted? | Methodology and current signatures |
| High availability | What state survives a failover? | Vendor failover design and test record |
Operate it as a control, not an appliance
Assign a rule owner, back up after approved changes, review stale exceptions, and test restoration. A powerful appliance with undocumented rules becomes harder to trust over time.
Operations should include configuration backups, software review, certificate renewal, log retention, administrator access review, and a tested replacement path. Record the last known-good version before an upgrade. If the appliance fails, the recovery plan should state how internet access and critical internal routes will be restored safely.
How to size a hardware firewall
During evaluation, run representative file transfers, calls, backups, and VPN sessions while the selected controls are active. Check latency, CPU or resource use, log detail, and configuration export. A successful speed test alone does not validate segmentation or recovery.
Example: sizing a gateway for a small office
A small office has a fast internet connection, remote workers, a guest network, cloud backups, and a local file server. Marketing material lists a high firewall throughput, but the office also wants intrusion prevention, VPN access, and logging enabled.
Choose capacity from measured evidence
Create a requirements sheet using real internet speed, expected VPN concurrency, inter-zone traffic, and the security services that will remain enabled. Compare feature-enabled performance and support life rather than the largest unqualified throughput figure.
Hardware firewall requirements checklist
- List internet, VPN, and inter-zone traffic separately.
- Confirm current firmware support and the expected replacement window.
- Verify configuration backup, restore, and local recovery access.
- Check whether logs can be retained and exported in a useful format.
- Assign ownership for updates, rules, certificates, and subscriptions.
Hardware firewall sizing mistakes
- Buying capacity from a raw routing number while planning to enable inspection features that have a different performance limit.
- Ignoring subscription and support expiry. A functioning appliance can become an operational risk when signatures, firmware, or assistance stop.
- Creating zones without documenting allowed communication. Segmentation names do not enforce useful policy by themselves.
Hardware firewall questions
Does a hardware firewall replace host firewalls?
No. The gateway controls traffic crossing its boundary. Host firewalls still protect devices on local, guest, or compromised networks and can make application-aware decisions.
What does next-generation firewall mean?
It is a broad product category commonly associated with application identification and additional inspection. Compare the exact documented capability and evidence rather than relying on the label.
How much spare capacity should I buy?
Allow for realistic growth and failover, but calculate it from enabled features and measured workloads. An arbitrary multiplier can waste money or still miss the true bottleneck.