
Current Firewall Reviews: Compare Security Gateways
Compare current Firewalla, Netgate, and UniFi gateways by ports, inspected throughput, management, support, and operating fit.
Updated October 31, 2026A firewall is a policy enforcement point. Start with the traffic and trust boundary you need to control, then choose the narrowest rule that solves the problem and verify the result.
Start with how a firewall evaluates traffic when the boundary or stateful behavior is still unclear.
When a policy already exists, use the firewall testing workflow to verify the intended allow and deny outcomes.
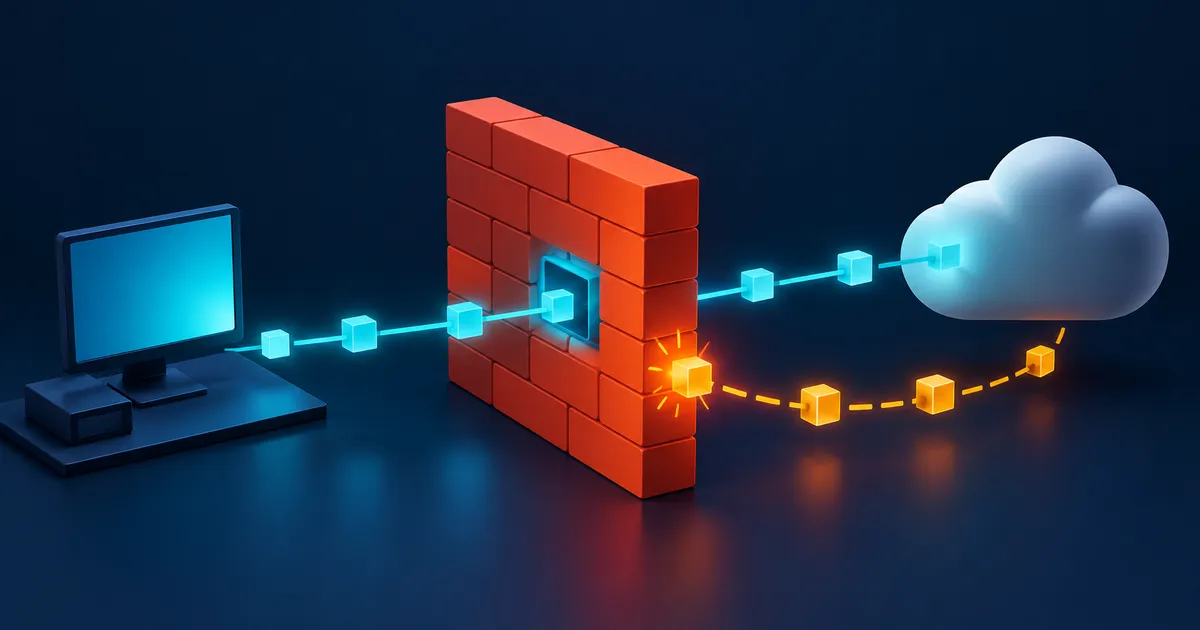
Match the control to the boundary that actually sees the traffic. A host firewall, router, and managed gateway solve different parts of the same path.
| Situation | Recommended starting point | Reason |
|---|---|---|
| One computer | Use the operating system firewall | Application-aware rules are usually easier to maintain than open ports. |
| Home network | Use the router firewall plus device firewalls | The router controls the boundary while each device protects itself on local networks. |
| Small office | Use a managed gateway and host firewalls | Logging, segmentation, backups, and a documented rule owner matter more than a long feature list. |
Use the mechanism guide for first principles, the software and hardware guides for selection, the testing guide for planned verification, and the troubleshooting guide when real traffic fails or bypasses policy.
Compare current Firewalla, Netgate, and UniFi gateways by ports, inspected throughput, management, support, and operating fit.
Updated October 31, 2026Compare maintained open-source firewall platforms by hardware scope, updates, packages, administration, recovery, and operator responsibility.
Updated October 31, 2026Learn how stateful, application, host, and network firewalls make traffic decisions and where their protection ends.
Updated October 31, 2026Compare built-in and third-party software firewalls using update, rule, logging, and recovery criteria.
Updated October 31, 2026Choose a hardware firewall using throughput, update support, segmentation, logging, and recovery needs.
Updated October 31, 2026Compare the best free firewall options for Windows, macOS, and Linux by platform, inbound protection, application control, maintenance, and fit.
Updated October 31, 2026Test a firewall with an expected-traffic matrix, correct vantage points, logs, rollback, and documented results.
Updated October 31, 2026Troubleshoot blocked, unexpectedly allowed, slow, or intermittent traffic by checking the service, path, policy, state, NAT, and logs in order.
Updated October 31, 2026Firewall work becomes easier to review when it follows the lifecycle of a rule rather than a product feature list.
Identify which networks, devices, applications, or users have different trust. A firewall placed at the wrong boundary cannot observe or control the communication you care about.
Describe source, destination, direction, protocol, service, owner, and purpose before opening a console. This turns a vague request into a rule another person can review.
Verify one allowed case and one blocked case, preserve the evidence, and set a review date. Remove the rule when the service or owner disappears.
Use the router or gateway at the internet boundary and host firewalls on computers. Each layer sees a different part of the communication path.
Rules without an owner, purpose, or expiry are difficult to justify and are likely to outlive the service they were created for.
Firewall recommendations are reviewed against NIST policy guidance, current platform documentation, and the operational evidence a reader can verify. Unsupported product-review URLs are consolidated into current selection criteria instead of retaining expired rankings.