
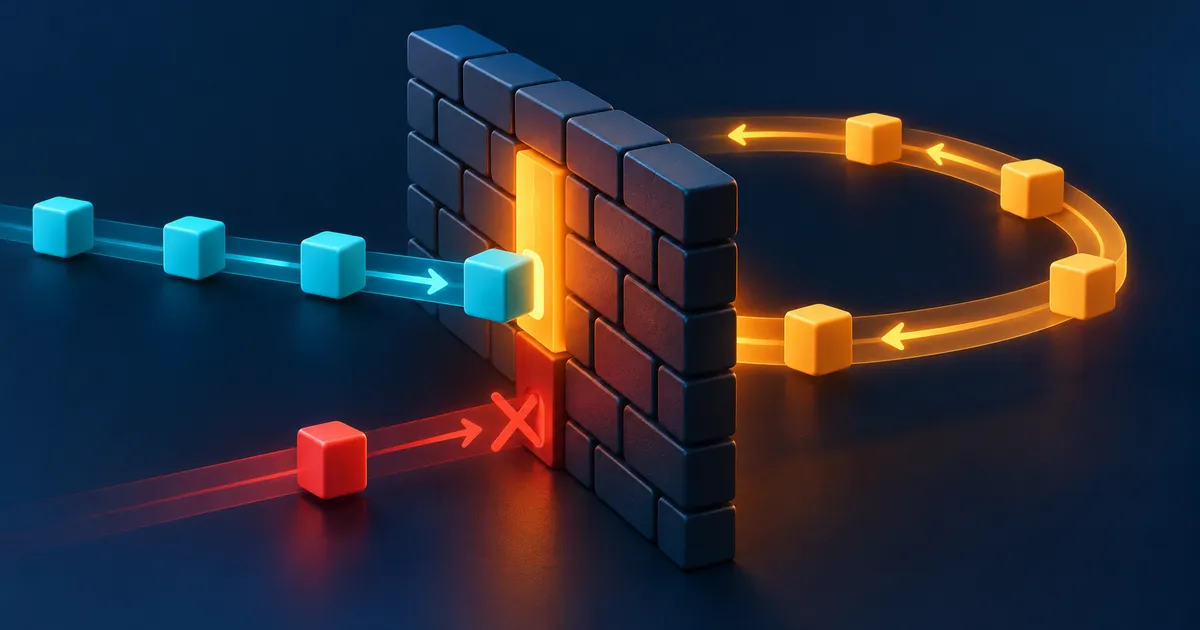
Firewall terms that describe different jobs
These terms are related, but they are not interchangeable. Naming the right control makes a rule easier to design, test, and explain.
Firewall
A firewall applies a traffic policy at a device, application, or network boundary. It allows, rejects, or drops traffic according to the information the rule can inspect.
Network address translation
NAT changes address or port information as traffic crosses a device. It can hide internal addressing, but the firewall policy still decides whether a new connection is accepted.
Stateful inspection
A stateful firewall records allowed connection state. Return packets can match that record instead of requiring a broad rule for unrelated inbound traffic.
Inbound and outbound
Inbound describes traffic entering the boundary being evaluated. Outbound describes traffic leaving it. The same packet can have a different direction at another device or zone.
Port and service
A TCP or UDP port is a number used by a transport connection. A registered service name is a clue, not proof of which program is listening on a system.
Network profile or zone
A profile or zone groups a network by trust and policy. A rule that is reasonable on a private home network may be unsafe on a public network.
Follow one connection through the decision
A new connection has a direction, protocol, source, destination, and service. A stateful firewall also remembers whether the packet belongs to a connection that was already allowed. This is why return traffic can work without a broad inbound rule.
Application-aware controls can attach a rule to a program or service. That is often safer and easier to retire than leaving a port open for every process.
A connection should be described from the viewpoint of the firewall that will evaluate it. A laptop may call the traffic outbound, while a server-side firewall sees the same exchange arrive inbound. Write the source, destination, protocol, port, direction, and network zone before deciding which rule applies.
- Default deny unsolicited inbound traffic at untrusted boundaries.
- Allow only the service, source, and destination the task requires.
- Log denials selectively so the signal remains useful.
Know which firewall type solves which problem
These firewall types can be combined because they inspect different evidence. A gateway can separate networks, a host firewall can identify the local application, and a web application firewall can evaluate HTTP requests. Adding a layer is useful only when its owner understands the traffic it is meant to control.
| Type | Useful boundary | Main limitation |
|---|---|---|
| Host firewall | One computer or server | Cannot control traffic that never reaches the host |
| Router or gateway firewall | Between networks | May not know which local application created traffic |
| Web application firewall | HTTP traffic to a web application | Does not replace host hardening or network controls |
Verify the policy instead of trusting a badge
Document the expected connection, test from the correct side of the boundary, and confirm both the allowed case and a blocked case. A passing internet port scan does not prove that local network segmentation or outbound policy is correct.
A complete test includes an expected allow, an expected denial, and the matching evidence. Capture the time, test source, destination, rule identifier, and observed result. If a test fails, this record helps distinguish a policy error from routing, name resolution, service availability, or an incorrect test location.
How a firewall evaluates traffic
Keep unsolicited internet traffic blocked at the router. On the laptop, allow only the printing application or required local printing service on the private network profile. If the network is segmented, permit the laptop to initiate the required printer service while blocking new connections in the reverse direction.
Example: allowing a printer without exposing the laptop
A laptop on a trusted home network needs to send print jobs to one network printer. The printer does not need to initiate connections to every computer, and nothing on the public internet needs to reach either device.
Confirm the intended traffic decision
Print a test document, confirm the firewall logs show the expected destination and service, and then try to initiate an unrelated connection from the printer network toward the laptop. The useful result is one working task plus a verified blocked path, not a general statement that the firewall is on.
Stateful firewall decision walkthrough
A stateful firewall does not judge an isolated packet in a vacuum. It evaluates where the traffic entered, whether policy permits a new connection, and whether later packets belong to recorded connection state.
| Stage | Question | Recorded evidence |
|---|---|---|
| Classify | Which interface, zone, address family, and direction apply? | Ingress interface and zone |
| Match state | Does this packet belong to an established allowed connection? | Connection tuple and state |
| Evaluate policy | Which first applicable rule covers the source, destination, protocol, and service? | Rule identifier and action |
| Act and record | Should the packet be allowed, rejected, or silently dropped? | Log action and reason |
Return traffic is allowed only when it matches tracked state or another explicit rule. State does not turn an unrelated inbound connection into a trusted one.
Firewall policy review checklist
- Name the source, destination, direction, protocol, and service.
- Identify whether the rule belongs at the device, gateway, application, or more than one layer.
- Choose the narrowest source and network profile that supports the task.
- Record who owns the rule and when it should be reviewed.
- Test one expected allow and one expected deny result.
Firewall mistakes that create hidden exposure
- Treating network address translation as the entire firewall policy. Address translation changes addressing, while the filtering policy decides which new connections are accepted.
- Opening a port on every network profile. A service needed at home may not be appropriate on airport, hotel, or other public networks.
- Testing only the permitted connection. A rule is not fully checked until a nearby connection that should remain blocked is also tested.
Firewall behavior questions
Does a firewall make antivirus unnecessary?
No. A firewall controls network communication according to policy. Endpoint protection, updates, restricted privileges, and safe recovery address different stages of an attack.
Is blocking every inbound connection always safer?
It reduces reachability but can break legitimate sharing, management, and accessibility services. The practical goal is to allow documented needs and block everything else.
Why can return traffic pass when inbound traffic is blocked?
A stateful firewall remembers an allowed connection and recognizes related response packets. A new unsolicited inbound connection has no matching allowed state.