
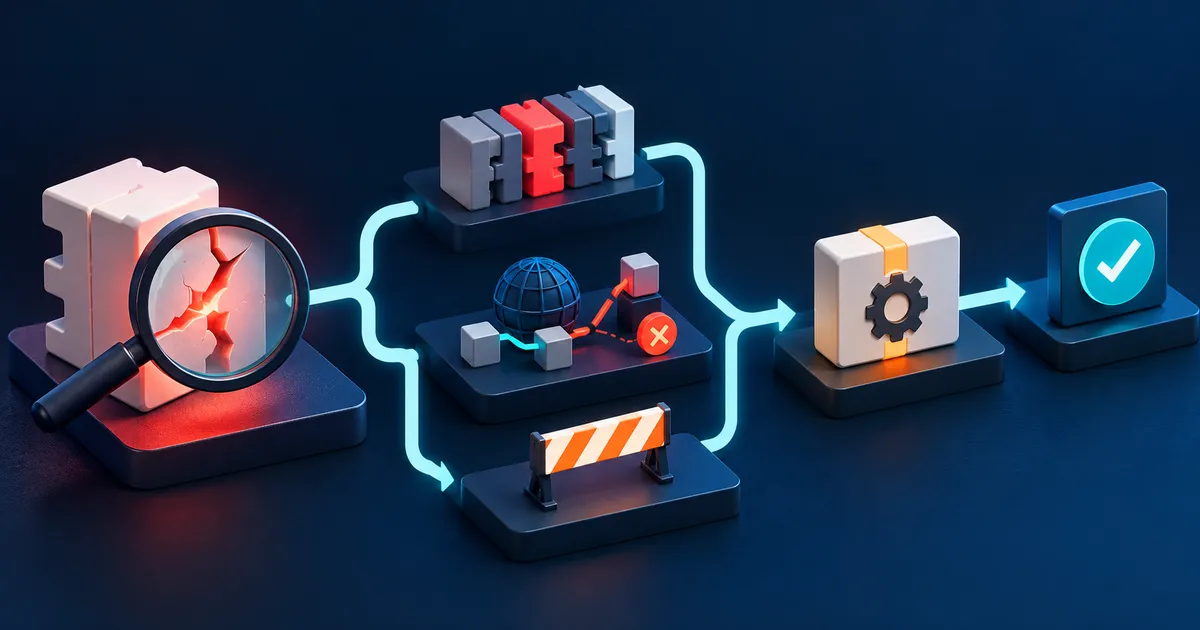
Zero-day exposure action checklist
- Identify exact product, component, version, and configuration.
- Check the original vendor advisory and known-exploitation evidence.
- Prioritize internet-facing, privileged, and sensitive systems.
- Document temporary containment, owner, impact, and removal condition.
- Verify the running fixed version and review for compromise evidence.
Zero-day exposure worksheet
Translate an alarming advisory into an asset decision. The product name alone is not enough because affected versions, enabled features, network reachability, identity controls, and active exploitation evidence can change the priority.
| Question | Record |
|---|---|
| Product and version | Exact edition, build, package, firmware, and deployment role |
| Applicability | Affected version range, required feature, configuration, and platform |
| Exposure | Internet, partner, user, or internal reachability and authentication |
| Exploitation evidence | Vendor advisory, CISA catalog status, observed indicators, and date checked |
| Mitigation | Disable feature, restrict source, isolate asset, increase monitoring, or remove route |
| Resolution and verification | Fixed version, update result, service state, logs, and repeated exposure test |
Turn a headline into a scoped decision
A generic product-family name can cause both panic and missed exposure. Asset inventory and version evidence are the bridge between an advisory and action.
Create an applicability record that names the affected product, installed version, enabled component, exposure, privilege, and business owner. Link each field to an inventory query, vendor advisory, or configuration check. This separates confirmed exposure from systems that merely share a product family name.
- Identify the exact product, component, version, and configuration.
- Check whether exploitation requires authentication or network reachability.
- Look for vendor mitigations and known side effects.
- Track the permanent update and remove temporary workarounds afterward.
Reduce exposure while preserving evidence
A temporary mitigation should name the capability it removes and the user impact it creates. Restricting network reachability, disabling a parser, or changing a service account can reduce risk while a fix is tested. Schedule removal of the workaround after patching so it does not become an undocumented permanent outage.
| Situation | Possible containment | Verification |
|---|---|---|
| Internet-facing service | Restrict source or disable the affected feature | Confirm the service is no longer reachable |
| Client-side flaw | Disable the risky handler or content type | Test normal workflows and the blocked path |
| Suspected compromise | Isolate the system without wiping it | Preserve logs and follow incident handling |
| Patch available | Test and deploy based on exposure | Confirm installed version and service health |
Avoid absolute product claims
No antivirus, firewall, or gateway can guarantee protection from every unknown exploit. Layered controls can reduce reachability, execution, privilege, and impact, which is a measurable and more honest objective.
Security controls may interrupt part of an exploit chain, but that is not the same as fixing the flaw. State which stage a control can observe or block and how that claim was tested. Keep monitoring for exploitation evidence until the affected version is updated and the mitigation has been verified.
How to scope a zero-day exposure
After updating, restart the application or device when required and verify the running version, not only the downloaded package. Remove temporary feature blocks after the permanent fix is confirmed, and investigate any indicators described by the advisory.
Example: a critical vulnerability headline names your browser
A security headline says a browser has an actively exploited zero-day flaw. Several computers use that browser, but automatic update status, exact versions, and exposure to the affected feature are not yet known.
Set the response from reachability and exploitation evidence
Start with the vendor advisory and an authoritative exploitation record. Inventory exact versions, confirm whether the fixed release is installed, and prioritize devices that handle sensitive accounts or browse untrusted content. Apply a documented mitigation only when the patch cannot yet be deployed.
Zero-day response mistakes
- Treating every vulnerability with a high score as equally urgent without checking reachability, exploitation, privileges, and asset importance.
- Assuming automatic updates mean the fixed version is active. Applications may require a restart, or an update channel may be delayed.
- Leaving emergency mitigations indefinitely. Workarounds can break features and create undocumented configuration debt.
Zero-day questions
Does zero-day mean nobody knows about the flaw?
It generally means defenders need to respond before a fix was available, but knowledge can differ among researchers, vendors, attackers, and the public.
Will a firewall block a zero-day exploit?
It can reduce reachability or block known behavior, but it cannot guarantee protection. The affected service, protocol, encryption, and attacker position determine what the firewall can observe.
Should every system be patched immediately?
Rapid patching is important for exposed exploited flaws, but safe deployment still requires applicability checks, backups, recovery planning, and verification.