
Bluetooth Security: Prevent Unauthorized Access
Protect phones, computers, cars, headphones, and smart devices from unsafe Bluetooth pairing, unwanted tracking, exposed services, and account compromise.
Updated October 31, 2026Threat labels matter less than the response path. Preserve evidence, isolate a suspected device when needed, secure affected accounts from a known-clean device, and verify recovery before reconnecting.
For a deceptive message or credential request, follow the phishing response decision path according to what was opened, entered, or executed.
If unwanted monitoring is suspected, use the spyware evidence and recovery guide before resetting a device or removing safety-sensitive evidence.
When a newly disclosed flaw may affect an exposed product, use the zero-day exposure response workflow to establish applicability, reduce exposure, and verify the mitigation.
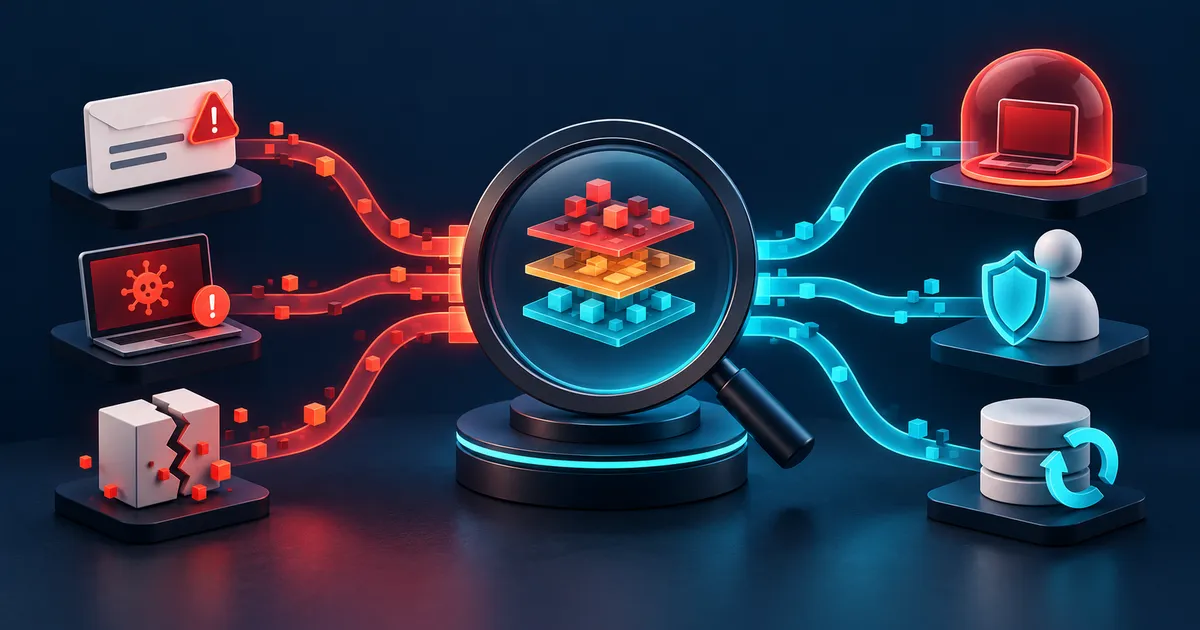
Choose the response from the evidence: seeing a message, entering credentials, running a file, and confirming account changes are different events with different consequences.
| Situation | Recommended starting point | Reason |
|---|---|---|
| Suspicious message only | Do not interact; report and delete | Verify the claimed request through a separate trusted channel. |
| Credentials were entered | Change the password from a clean device | Revoke sessions, enable strong MFA, and review recovery methods. |
| A file ran or a device behaves abnormally | Disconnect the device from networks | Preserve the alert details and follow an incident or recovery process. |
Open the guide that matches the event or control you need now. Each guide separates weak signals from stronger evidence and ends with a way to verify recovery.
Protect phones, computers, cars, headphones, and smart devices from unsafe Bluetooth pairing, unwanted tracking, exposed services, and account compromise.
Updated October 31, 2026Learn when Bluetooth access can become a home-network attack, which devices create a bridge, how to contain it, and why changing a MAC address is not a fix.
Updated October 31, 2026Use a separate trusted channel to verify urgent messages, and follow clear steps after a click, download, or credential entry.
Updated October 31, 2026Understand what zero-day means, how vendors communicate active exploitation, and how to reduce exposure before and after a patch.
Updated October 31, 2026Reduce unwanted messages, recognize fraud patterns, and respond without confirming your address to abusive senders.
Updated October 31, 2026Recognize evidence of unwanted surveillance software, isolate risk, preserve evidence, and recover accounts and devices safely.
Updated October 31, 2026Understand how trojans disguise execution and use layered controls to prevent, contain, and recover from infection.
Updated October 31, 2026Compare the best antivirus software for Windows in 2026 using current independent evidence, false-positive results, operational fit, privacy, and recovery.
Updated October 31, 2026Choose privacy controls by identifying who can observe, link, retain, or misuse your data in a specific activity.
Updated October 31, 2026Secure a personal phone with supported updates, strong unlocking, app-permission review, account recovery, and safer network habits.
Updated October 31, 2026Use the built-in macOS firewall, safer app sources, updates, permissions, backups, and account controls without relying on outdated security-suite rankings.
Updated October 31, 2026Threat names can be confusing. A consistent response model helps you act according to evidence and consequence instead of fear.
Separate seeing a message, opening a page, entering credentials, running a file, and observing confirmed account or device changes. Each stage needs a different response.
Use a known-clean device for important account changes. Secure primary email and recovery methods before lower-value accounts, because they can reset everything else.
Keep relevant alerts, timestamps, sessions, filenames, and transaction details. After containment, verify account, device, and backup integrity rather than assuming one scan resolved the incident.
Disconnect it when unknown software executed, compromise is likely, or continued communication could spread harm. Preserve evidence and avoid wiping it blindly.
Start with the primary email and recovery accounts that can reset other services, followed by financial, work, and high-impact accounts.
Response advice is checked against current security-agency guidance, platform documentation, and the sequence of evidence, containment, account recovery, and verification. It does not promise that one product detects every threat.